Security
Security you can inspect, described without exaggeration
Invoice data is commercial and tax data. This page lists the controls that protect it in Invoice And Tax — what they do, and where their limits are.
Last reviewed:
How does Invoice And Tax protect my data?
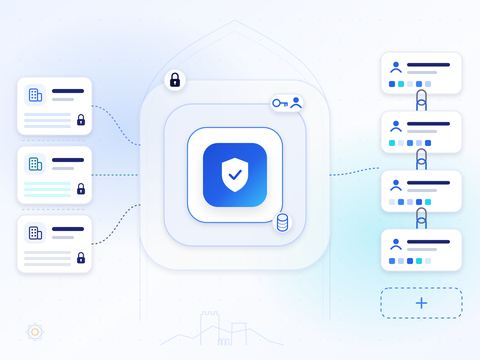
Access is role-based; multi-factor authentication is available for every user and mandatory for administrators; sensitive fields are encrypted at rest; each organisation's and branch's data is isolated; validation is deterministic; and every significant action is recorded in an append-only audit trail.
Accreditations and certifications
-
Accredited Service Provider
Invoice And Tax is listed by the Oman Tax Authority's Fawtara portal as an Accredited Service Provider.
View evidence: Accredited Service Provider Verify with issuer(opens external site)
-
AP Certified
Peppol-certified Access Point Service Provider.
View evidence: AP Certified Verify with issuer(opens external site)
-
ISO/IEC 27001:2022
Invoice And Tax is developed and operated by Elsayed Hamdi for Advanced Technology SPC, whose Information Security Management System is certified to ISO/IEC 27001:2022 for the scope stated in certificate 305026071423IS.
Controls
Controls in the platform
-
Multi-factor authentication
Multi-factor authentication available for every user; mandatory for administrators. Recovery codes are provided when you enrol.
-
Role-based access control
Permissions follow roles, so each person sees and does only what their job requires.
-
Encryption at rest
Sensitive fields are encrypted at rest in the database, not only on disk.
-
Tenant isolation
Data is separated by organisation and branch. A user who belongs to several organisations switches context explicitly.
-
Append-only audit trail
Create, approve, issue and adjust actions are written as audit events that are never edited in place.
Audit and governance: Append-only audit trail -
Deterministic validation
Versioned rules mean the same document always gets the same result, and you can tell which rule set was applied.
Defence in depth
Protection in layers
Each control on this page protects a different layer: access is role-based with multi-factor authentication, sensitive fields are encrypted at rest, each organisation's and branch's data is kept separate, and every significant action is recorded in an append-only audit trail.
Document exchange
Protected in transit
Exchange over the Peppol network uses the AS4 messaging protocol, under which each message is signed and encrypted between access points. Invoice And Tax is a Peppol-certified Access Point Service Provider. The platform and its API are served over encrypted connections.
- AS4 messages signed and encrypted between access points
- Organisation-scoped API keys, shown once at creation
- Each organisation's data kept separate
Accountability
Every action leaves a trace
Issued documents are frozen snapshots. Corrections happen through credit notes, debit notes or reversing entries — never by overwriting history. Approvals for VAT returns use a maker/checker step, and all of it appears in the audit trail.
- Issued versions cannot be edited
- Maker/checker approval for VAT returns
- Audit events record who, what and when
Responsible disclosure
Reporting a security issue
If you believe you have found a security vulnerability in Invoice And Tax, please tell us privately through our contact page, marking your message “Security”. Include what you found and how to reproduce it, and avoid accessing data that is not yours. We will acknowledge your report and keep you informed while we investigate.
Security questions
Is multi-factor authentication mandatory?
It is available for every user and mandatory for administrators.
Where is our data kept separate from other customers?
Data is isolated per organisation and branch inside the platform. Private-cloud and on-premises deployment is also available when your policy requires it.
Where is the hosted service's data located?
Hosted service data is stored in Germany or the Sultanate of Oman, depending on the client's preference, as we operate multiple servers.
Can someone change an issued invoice?
No. Issued versions are frozen. Changes are made through credit or debit notes linked to the original, and every action is in the audit trail.
Can we receive security documentation for our review?
Yes. Contact us and tell us what your review requires.